Toolkit 5 - Unified AI & Security Risk System
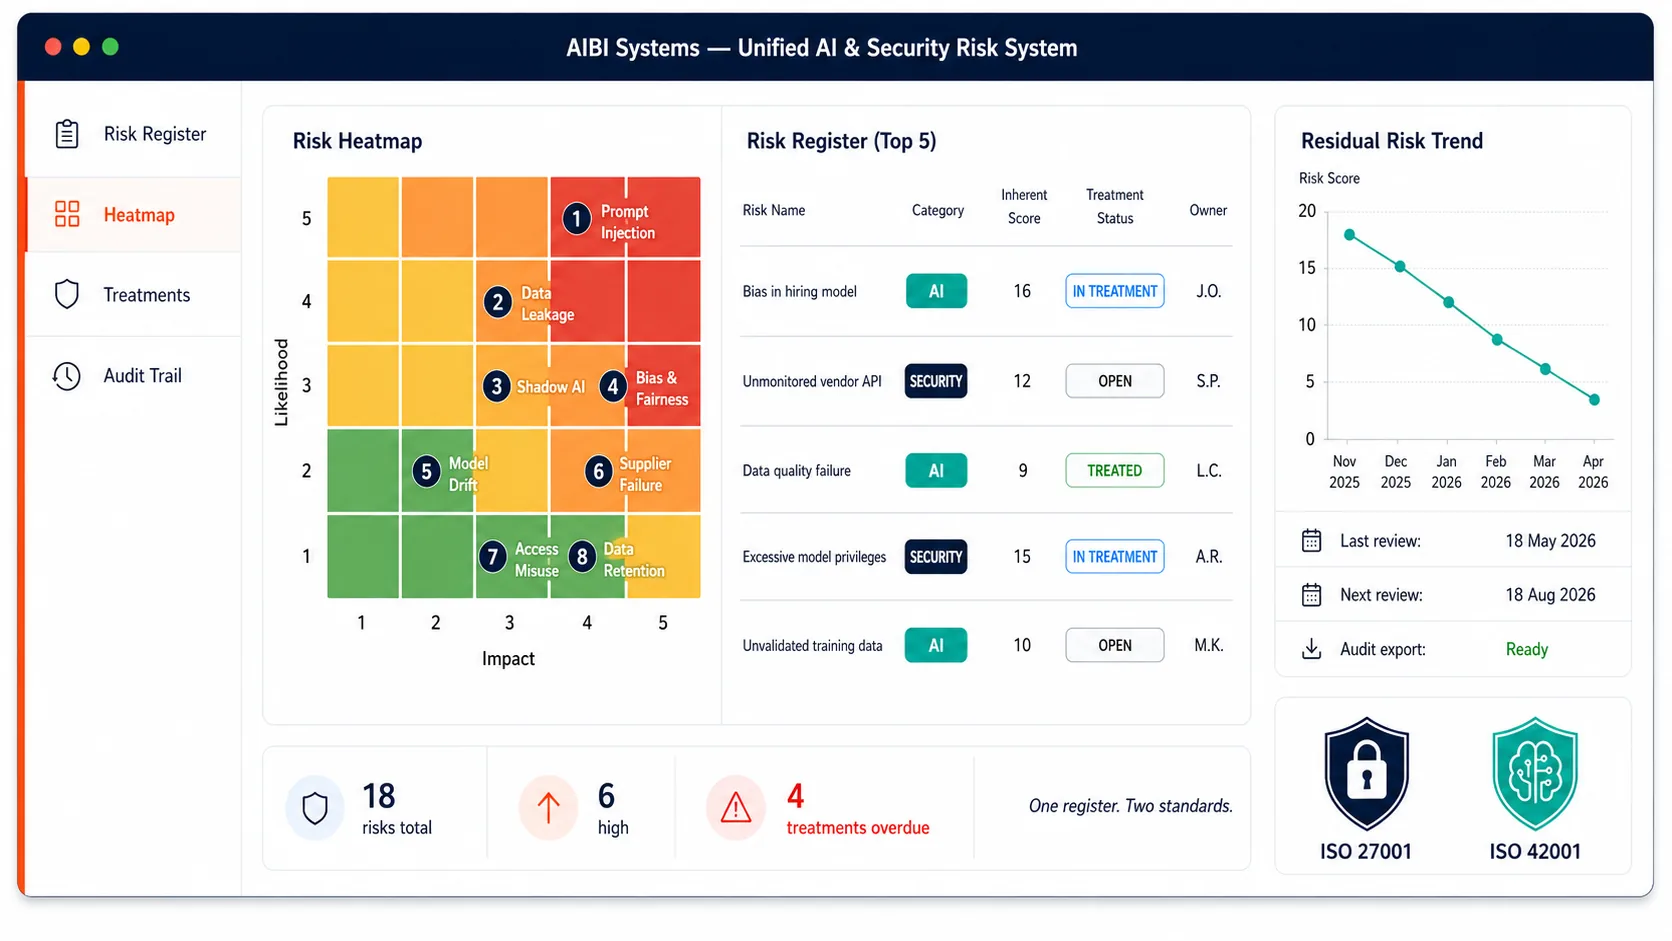
Built on the Build Once. Comply Twice.™ principle - one risk method, one scoring scale, one evidence spine that works across both ISO 27001 and ISO/IEC 42001.
Designed for organisations that already run an ISMS risk process and need AI risk integrated properly.
Available now
Paying by invoice or need a PO raised first? Request an invoice →
We'll send you a proforma invoice within 1 business day. Access is provided once payment clears, using the same automated delivery as a card purchase.
🔒 Secure checkout via Lemon Squeezy ⚡ Instant delivery to your email 📄 7-day refund policy 🧾 Price includes UK VAT 👤 Your governance data stays with you
Outputs may be shared with auditors, customers, regulators, and advisers for assurance.
After using this toolkit you will have
- One risk register for security and AI risks - no parallel processes, no competing registers
- Consistent 1-5 scoring across InfoSec and AI lifecycle risks with a clear Low / Medium / High / Critical banding
- Residual risk acceptance recorded at the right level, with Critical risk signed off by the Risk Owner, the CISO / AI Governance Lead and the Board or Executive Sponsor
- Named risk owners with a charter and RACI, so treatment and review duties are explicit
- An AI incident log that feeds back into the risk position
- A clean audit trail: every risk entry links to evidence, and every AI risk links to its AI system through one System ID (for example AI-001)
Designed for
- Organisations already running an ISMS risk process that need AI risk integrated properly
- Risk owners and governance leads who need repeatable, defensible assessments
- Internal audit teams needing traceability from risk to controls to evidence
- GRC, InfoSec, and AI governance leads
- Teams consolidating multiple risk registers and AI governance spreadsheets
What this replaces
Most organisations running an ISMS have an established risk register. When AI governance requirements arrive, the typical response is to create a separate AI risk spreadsheet alongside it.
The result is two registers with different scoring scales, different owners, different evidence expectations, and no clean narrative connecting them at audit.
This toolkit replaces that with one unified risk architecture: the same 1-5 scoring model, the same treatment framework, and evidence hooks that trace from any risk entry back to a physical artefact in your evidence library.
The risk scoring model covers six categories:
- InfoSec
- AI Lifecycle (bias, drift, misuse, model failure, performance degradation)
- AI Ethics (transparency, fairness, contestability)
- AI Transparency
- Supplier (third-party AI tools and embedded AI features)
- Operational
It is not a certification scheme and does not guarantee certification outcomes. It supports practical governance and audit-ready evidence across both standards.
How it works
Run the risk process (first pass)
- Open the Unified Risk Register and review the HOME tab - scoring model, categories, and navigation
- List the AI systems in scope and give each one a System ID (AI-001, AI-002 and so on). If you use Toolkit 6, take the IDs from its AI inventory
- Record the System ID and any AISIA reference against each AI risk in the AI_System_ID / AISIA column
- Enter risk entries in the Risk Register with scores, owners, and evidence IDs
- Complete treatment plans in the Risk Treatment Plan tab
- Use the Export_Audit_Pack sheet for stakeholder reporting and audit preparation
Ongoing operations
- Review each risk at the more frequent of its category cadence and its residual band cadence
- Use the Risk Acceptance Form whenever residual risk sits above appetite
- Log AI incidents in the AI Incident Log and update the affected risk entries
- Keep the SoA lite views for ISO/IEC 42001 and ISO 27001 aligned with treatment decisions
- Use the Customer Assurance One-Pager to answer customer questions with practices you can evidence
Everything included - 11 files
Contents at a glance: 4 read-only guides, 1 risk workbook, 5 editable templates and the licence terms. 5 PDF, 5 DOCX and 1 XLSX.
Toolkit 5 is the risk governance layer: criteria, scoring, register, treatment, residual acceptance, risk owners and incidents. The AI inventory, AISIA forms, model cards and lifecycle stage records are in Toolkit 6 - AI Lifecycle Control System, or get both in the AI Risk & Lifecycle Control bundle.
Read-only guides
-
Start Here - Toolkit 5 PDF
Orientation guide, file sequence and first steps.
-
Product Master Guide - Toolkit 5 PDF
Full customer guide for implementing the unified risk method.
-
Quickstart - 60 Minutes - Toolkit 5 PDF
Timed guide for the first working session.
-
Auditor Orientation Sheet - Toolkit 5 PDF
Read-only briefing for audit and assurance stakeholders.
Risk workbook
-
Unified Risk Register XLSX
Risk criteria, unified 1-5 scoring, the risk register with an AI system link column, treatment plan, SoA lite views for ISO/IEC 42001 and ISO 27001, and an audit pack export.
Editable templates
-
Document Control Blocks DOCX
Metadata and version control blocks in four layouts for your governance records.
-
Risk Acceptance Form DOCX
Records residual risk acceptance with sign-off levels by risk band.
-
Risk Owner Charter and RACI DOCX
Defines risk owner duties, reporting lines and accountability.
-
AI Incident Log Template DOCX
Captures AI incidents, notification timings and the resulting risk updates.
-
Customer Assurance One-Pager DOCX
A customer-facing summary of how you govern AI and security risk.
Licence
-
Licence, Use, Refund and IP Terms - Toolkit 5 PDF
Read-only licence and permitted-use reference.
Sample preview slice
This preview describes the output structure without exposing the scoring method, workbook mechanics or implementation engine.
- Unified risk register view with owners, treatment status, review cadence and evidence IDs.
- Risk acceptance route showing who signs off each residual risk band.
- AI system link column that connects each AI risk to its System ID and AISIA reference.
Outputs and evidence you can generate
- A unified risk register with consistent scoring rationale across security and AI
- Treatment plans with owners, deadlines, and implementation status
- Residual risk visibility and review cadence evidence
- Signed risk acceptance records for residual risk above appetite
- Risk owner charter and RACI showing who is accountable for each risk
- An AI incident log linked to the affected risk entries
- Statement of Applicability lite views for ISO/IEC 42001 and ISO 27001
- Audit trail: approvals, actions, monitoring triggers, and exceptions all traceable to Evidence IDs
Where it fits in the system
Toolkit 5 is the operational governance engine. It connects policy intent (Toolkit 4) to real-world controls and evidence, and gives auditors a clean narrative: risks are identified, assessed, treated, and reviewed.
Every risk entry includes an evidence reference field that maps directly to your evidence library and, if you use Toolkit 2, to the evidence mapping area in the Integration Engine.
Toolkit 5 governs AI risk. Toolkit 6 - AI Lifecycle Control System proves AI systems remain controlled. Each AI risk records the System ID (for example AI-001) and AISIA reference from Toolkit 6, or from your own inventory and impact assessments, so the two toolkits connect without duplicating any records. Both work standalone.
Licence summary (plain English)
- Licensed to a single legal entity (the purchasing organisation)
- Authorised users include employees and individual contractors acting on your behalf
- Outputs may be shared with auditors, customers, regulators, and advisers for assurance
- Toolkit files may not be shared, resold, or reused as a commercial method across other organisations
When this is not for you
- You want a lightweight list without governance ownership - this is a real risk system that requires maintained entries, owners, and review dates
- You do not intend to review and update risks - registers must be maintained to be effective and credible
- You want a technical model testing tool rather than governance risk management
- You want certification guarantees rather than risk evidence and structure
Procurement justification
This purchase supports development of a more consistent AI and information security risk management approach.
The toolkit provides reusable risk assessment structures, a unified risk register, treatment and acceptance workflows, incident logging and evidence templates intended to support more defensible and traceable governance activity.
The materials can be implemented internally by risk, information security, AI governance, data, compliance and internal audit teams to link AI systems, risk assessments, treatment actions, acceptance decisions, owners and evidence records.
This is a one-off digital toolkit purchase. The supplier does not require access to our AI systems, datasets, prompts, models, customer records, source code, production environments, internal systems, risk registers or completed evidence to fulfil this purchase.
The purchase is proportionate because it provides a common risk method for AI and security activity, reducing duplication across separate risk spreadsheets, acceptance records and treatment logs.
Designed for internal approval and governance workflows.
Frequently asked questions
Is this only for AI risks?
No. It is designed to unify information security risks and AI lifecycle risks in one register. The scoring model and treatment framework apply equally to both.
Does it include example AI risks?
Yes. The register includes worked example risks across information security, AI and supplier categories, with scores, owners, treatment and review dates filled in, so you can see how a completed entry should look.
Does Toolkit 5 include AI impact assessment (AISIA) forms?
No. The AISIA triage and full assessment forms, the AI inventory, model cards and lifecycle stage records are in Toolkit 6 - AI Lifecycle Control System. Toolkit 5 records the AISIA reference against each AI risk, so it works with Toolkit 6 or with your own impact assessments.
Can we use our existing risk scoring model?
You can, but the value is strongest when scoring is consistent across security and AI. The unified 1-5 model is designed to be directly compatible with standard ISMS risk scoring approaches.
How does this link to Toolkit 2?
Risk entries include an evidence reference field that maps directly to artefacts in your evidence library and to the evidence mapping area in Toolkit 2. This creates a three-step audit trace: control, then risk, then evidence.
Is this a certification scheme?
No. It supports ISO 27001 and ISO/IEC 42001 alignment and produces audit-ready artefacts, but does not constitute certification or guarantee certification outcomes.
How does payment work and who processes it?
Payment is processed securely by Lemon Squeezy, who act as merchant of record for AIBI Systems. Your payment, VAT collection, and any post-sale compliance are handled directly by Lemon Squeezy. Your download link is delivered to your email immediately after payment. All prices shown are inclusive of VAT.
Do I have to upload my governance data to AIBI Systems?
No. The paid toolkits are downloadable files that you use inside your own organisation. When you use them internally, AIBI Systems does not host, access, process or monitor your completed AI inventories, risk registers, assessments, policies or evidence records. Your governance evidence remains under your control.
Is AIBI a GRC platform?
No. AIBI is a practical toolkit and implementation system. It helps you structure AI governance, evidence and ISO 27001 to ISO/IEC 42001 alignment without requiring a new platform.
Can I use AIBI with our existing systems?
Yes. The toolkits can be used to support or inform your existing ISMS, SharePoint library, Microsoft 365 environment, GRC platform, audit evidence folder or internal governance process. There is no requirement to migrate your controls, risks or documents into a new system.
Does AIBI replace consultants or auditors?
No. AIBI provides structured implementation materials. You can use them independently, with your internal team, with a consultant, or as preparation for audit and assurance conversations.
Best pairing: AI Risk & Lifecycle Control bundle
Toolkit 5 gives you the AI risk method. Toolkit 6 gives you the lifecycle evidence trail: AI inventory, AISIA, model cards and stage-gated lifecycle records. Together they connect every AI system to scored risk, treatment and residual acceptance.
Toolkit 5 also appears in AI Governance Starter and AI Ethics & Risk. This page highlights AI Risk & Lifecycle Control because it is the strongest operational pairing for TK5.
Or get Toolkit 1 through Toolkit 6 in the Complete System Bundle.
Toolkit 5 - Unified AI & Security Risk System
One risk register for information security and AI lifecycle risks.
Instant download. One-off purchase. Outputs may be shared with auditors, customers, regulators, and advisers for assurance.